
Global Exception Handling in .NET: Complete Guide with Middleware and Best Practices
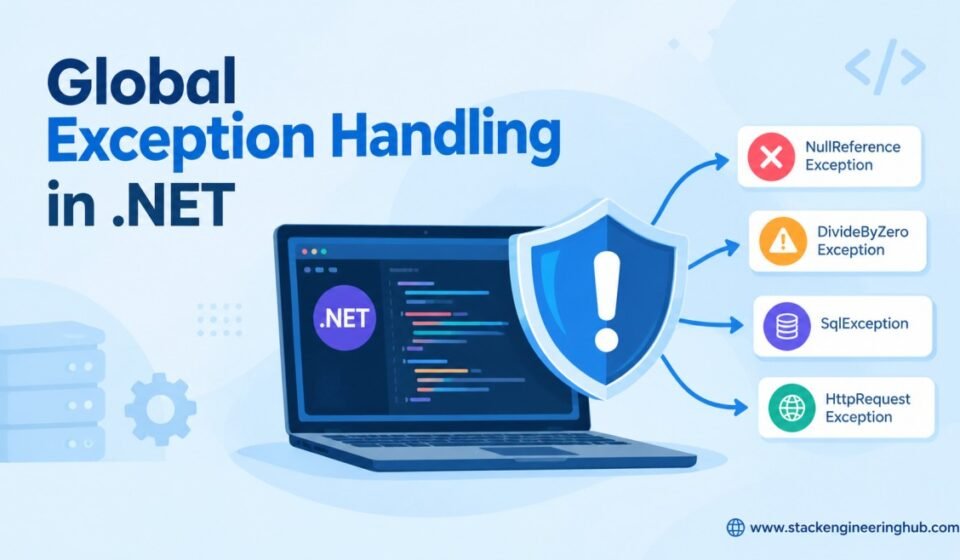
Global exception handling in .NET is an important part of building reliable, secure, and maintainable applications. Exceptions can occur because of invalid input, database failures, unavailable external services, programming errors, configuration problems, or unexpected runtime conditions. If every controller, service, or API method handles exceptions independently, the application can quickly become difficult to maintain. A centralized exception handling strategy provides a consistent way to catch unexpected errors, log useful diagnostic information, return appropriate responses, and protect sensitive implementation details from users. In modern .NET and ASP.NET Core applications, middleware is one of the most effective approaches for implementing centralized exception handling. This guide explains how global exception handling works, how to implement custom exception middleware, how to return consistent API responses, and which practices developers should follow in production applications.
What Is Global Exception Handling in .NET?
Global exception handling means handling unexpected exceptions at a centralized location instead of writing separate exception-handling code throughout the application. In a typical ASP.NET Core application, an HTTP request passes through several components such as middleware, authentication, authorization, controllers, services, repositories, and external integrations. An exception can occur at almost any point in this request pipeline.
Without centralized handling, developers may end up adding try-catch blocks to many controller actions. Although try-catch is useful when an application can recover from a specific failure, using it everywhere often creates duplicated code and inconsistent error responses. Global exception handling allows unexpected exceptions to reach one centralized component where they can be logged and converted into a safe response.
For ASP.NET Core developers, middleware is particularly useful because middleware can observe requests and responses while also catching exceptions generated by downstream components.
Why Global Exception Handling Is Important
A production application should not expose raw exception messages, stack traces, database details, file paths, or internal configuration information to users. Such information may help an attacker understand the application’s internal architecture. A centralized exception handler provides a controlled boundary between internal errors and public responses.
Global exception handling also improves maintainability. Instead of implementing the same logging and response-generation logic in multiple controllers, developers can maintain the behavior in one location. When the response format or logging strategy changes, the centralized handler can be updated without modifying every API endpoint.
- Provides consistent error responses.
- Reduces duplicated try-catch code.
- Centralizes exception logging.
- Prevents sensitive information from being exposed.
- Makes production troubleshooting easier.
- Improves API consistency and maintainability.
Global Exception Handling Using Middleware
ASP.NET Core applications use a middleware pipeline to process HTTP requests. Middleware components execute in a defined order, and each component can perform work before and after calling the next component. This makes middleware a natural location for catching unhandled exceptions.
A simple custom exception middleware can wrap the next request delegate inside a try-catch block. If downstream code throws an exception, the middleware catches it, records the exception using the logging framework, and creates a suitable HTTP response.
public class ExceptionMiddleware { private readonly RequestDelegate _next; private readonly ILogger<ExceptionMiddleware> _logger; public ExceptionMiddleware( RequestDelegate next, ILogger<ExceptionMiddleware> logger) { _next = next; _logger = logger; } public async Task InvokeAsync(HttpContext context) { try { await _next(context); } catch (Exception ex) { _logger.LogError(ex, "An unexpected error occurred."); context.Response.StatusCode = StatusCodes.Status500InternalServerError; context.Response.ContentType = "application/json"; await context.Response.WriteAsync( "An internal server error occurred."); } } }
The middleware calls _next(context) to continue processing the request. If a controller, service, repository, or another downstream middleware throws an exception, execution moves to the catch block. The exception is then logged and a controlled response is returned to the client.
Registering Custom Exception Middleware
After creating the middleware, it must be registered in the ASP.NET Core request pipeline. The middleware should be positioned early enough to observe exceptions generated by the components that follow it.
var builder = WebApplication.CreateBuilder(args); builder.Services.AddControllers(); var app = builder.Build(); app.UseMiddleware<ExceptionMiddleware>(); app.UseHttpsRedirection(); app.UseAuthorization(); app.MapControllers(); app.Run();
The exact middleware order depends on the application architecture. However, an exception handler intended to capture errors from downstream components should generally be registered near the beginning of the pipeline. Developers should also test the pipeline carefully when authentication, authorization, static files, routing, and custom middleware are involved.
Returning a Consistent API Error Response
A global exception handler should not simply return a plain text error message for every situation. APIs benefit from a predictable response structure because client applications can process errors consistently. A common approach is to return information such as the HTTP status code, title, message, and optionally a trace or correlation identifier.
{ "status": 500, "title": "Internal Server Error", "message": "An unexpected error occurred.", "traceId": "00-abc123-example" }
The public response should contain enough information for the client to understand the result without exposing internal implementation details. Detailed exception information should remain in application logs rather than being returned directly to users.
For modern ASP.NET Core APIs, developers can also use the ProblemDetails approach to provide standardized HTTP API error responses. This can make error handling easier for different clients and services consuming the API.
Handling Different Types of Exceptions
Not every exception should produce the same HTTP status code. A robust global exception handler should distinguish between known application exceptions and unexpected system failures. For example, a resource-not-found exception can map to HTTP 404, while a validation-related application exception may map to HTTP 400.
404 Not Found
A 404 response is appropriate when a requested resource does not exist. For example, if an API requests a product using an ID that is not present in the database, the application can return a controlled not-found response.
400 Bad Request
A 400 response is commonly used when the request is invalid or the supplied data does not satisfy application requirements. Validation failures should normally be handled as client errors rather than unexpected server exceptions.
401 Unauthorized
A 401 response indicates that authentication is required or the supplied authentication credentials are not valid. Authentication failures should not be converted into generic 500 responses.
403 Forbidden
A 403 response indicates that the request was understood but the authenticated user does not have permission to perform the requested operation.
500 Internal Server Error
A 500 response is appropriate for unexpected server-side failures that cannot be safely classified as a client error. The detailed exception should be logged internally while the client receives a generic production-safe message.
Creating Custom Exceptions
Custom exceptions can make business logic easier to understand. Instead of throwing a generic Exception for every business failure, an application can define specific exception types that represent meaningful domain conditions.
public class ProductNotFoundException : Exception { public ProductNotFoundException(string message) : base(message) { } }
The global exception handler can then identify this exception and convert it into an appropriate HTTP response. This approach separates business rules from response-generation logic and keeps controllers relatively clean.
Global Exception Handling and Logging
Exception handling and logging should work together. Catching an exception without recording useful diagnostic information can make production troubleshooting extremely difficult. When an unexpected exception occurs, the logging system should capture the exception object and relevant contextual information.
_logger.LogError( ex, "Unexpected error while processing request {Path}", context.Request.Path);
Logging the complete exception object is important because it preserves the exception message and stack trace for developers and operations teams. However, logs should also be reviewed for sensitive information. Passwords, authentication tokens, connection strings, personal data, and other confidential values should never be written unnecessarily to logs.
For a deeper discussion of structured logging and monitoring, see Logging in ASP.NET Core: Complete Guide to Structured Logging and Monitoring.
Try-Catch vs Global Exception Handling
Global exception handling does not mean that try-catch blocks should never be used. The two approaches solve different problems. A global exception handler is useful for unexpected failures that need centralized processing. A local try-catch block is useful when a specific piece of code can recover from an exception or when the application needs to perform a special operation before continuing.
For example, a service that communicates with an external system may catch a specific timeout exception, retry the operation, and then either return a result or throw a meaningful application exception. A controller should generally not need to repeat the same catch-and-return-500 logic for every action.
A good rule is to catch exceptions where the application can actually do something useful with them. Otherwise, allow the centralized exception handling mechanism to process unexpected failures.
Security Best Practices for Exception Handling
Exception responses are part of an application’s security boundary. Returning detailed internal exception information can reveal database structures, server paths, framework details, SQL statements, or other information that should remain private.
- Do not return stack traces in production responses.
- Do not expose database connection strings.
- Do not return internal file paths.
- Do not expose authentication tokens or secrets.
- Log detailed exceptions securely on the server.
- Return generic messages for unexpected production failures.
- Use meaningful HTTP status codes.
Development environments can provide more detailed diagnostic information because developers need it during debugging. Production environments should use controlled error responses and secure logging instead.
Global Exception Handling in Web APIs
Global exception handling becomes especially valuable in REST APIs because an API may have dozens or hundreds of endpoints. Returning different error formats from different controllers makes client-side development unnecessarily complicated.
A centralized handler allows every endpoint to follow the same response conventions. For example, a mobile application, JavaScript frontend, or another backend service can expect a consistent JSON structure when an error occurs. This reduces client-side special cases and makes API integration easier.
You can also review REST API Best Practices for Secure and Scalable APIs for related API design considerations.
Common Mistakes to Avoid
- Adding identical try-catch blocks to every controller action.
- Returning exception.Message directly to users.
- Returning stack traces from production APIs.
- Logging sensitive information such as passwords or tokens.
- Returning HTTP 500 for validation errors.
- Using inconsistent JSON error formats across endpoints.
- Ignoring exceptions without logging them.
- Creating custom exceptions without a clear business purpose.
Another common mistake is treating every failure as an unexpected server exception. Validation errors, authentication failures, authorization failures, missing resources, and unexpected infrastructure failures have different meanings and should be represented accordingly.
Global Exception Handling and Dependency Injection
Custom exception middleware can use dependency injection to access services such as ILogger, configuration providers, telemetry components, or application-specific services. This keeps the middleware testable and avoids creating dependencies manually inside the exception handler.
For developers working with larger ASP.NET Core applications, understanding dependency injection is useful because middleware, controllers, services, repositories, and other components commonly depend on registered services. You can learn more in Dependency Injection in ASP.NET Core.
Production Checklist for Global Exception Handling
- Create a centralized exception-handling strategy.
- Register exception middleware early in the request pipeline.
- Log unexpected exceptions with sufficient diagnostic context.
- Map known application exceptions to appropriate HTTP status codes.
- Return consistent JSON or ProblemDetails responses.
- Hide stack traces and internal implementation details in production.
- Protect logs from sensitive information.
- Test errors from controllers, services, databases, and external APIs.
- Monitor production exceptions and investigate recurring failures.
Official Microsoft Documentation
Microsoft provides official documentation covering error handling in ASP.NET Core, including built-in exception handling middleware and related techniques. Developers should refer to the official documentation when implementing exception handling for a specific .NET or ASP.NET Core version.
Microsoft ASP.NET Core Error Handling Documentation
Conclusion
Global exception handling in .NET provides a clean and reliable way to manage unexpected application failures from a centralized location. Instead of repeating exception-handling logic across controllers and services, developers can use middleware to catch unexpected exceptions, log diagnostic information, and return consistent responses to API clients. This improves maintainability while also reducing the risk of exposing sensitive internal information.
A production-ready strategy should combine centralized exception handling, meaningful HTTP status codes, structured logging, custom exceptions where appropriate, standardized API responses, and secure error messages. Try-catch blocks should still be used when an application can recover from a specific failure, but unexpected exceptions should normally flow to the global handler. With these practices in place, .NET applications become easier to troubleshoot, safer to operate, and more consistent for both developers and API consumers.

[…] handling can keep individual endpoints focused on normal application behavior. Our guide to Global Exception Handling in .NET explains a centralized approach for […]